The Assumptions in the Boardroom
What a week at the Private Directors Association PRISM Conference revealed about how directors think, challenge strategy, and govern a business environment that keeps changing.
I spent this week at the Private Directors Association’s PRISM Conference in Atlanta, having some interesting conversations about how boards make decisions.
The agenda covered familiar territory: strategy, performance, governance, risk, and leadership. AI was part of nearly every conversation, whether explicitly on the agenda or not.
What interested me most was how often we came back to the same underlying issue: the ability of a board to make good decisions when the environment, the information available, and the consequences of getting it wrong are all changing.
It’s a question that applies equally to a board evaluating its own effectiveness, a company pursuing a growth strategy, or a leadership team deploying AI.
And it starts with understanding how we think.
Director, Defined: What do you bring to the boardroom?
I had the opportunity to present Director, Defined: Your Board Archetype alongside Marva Bailer, Founder and CEO of Qualaix.
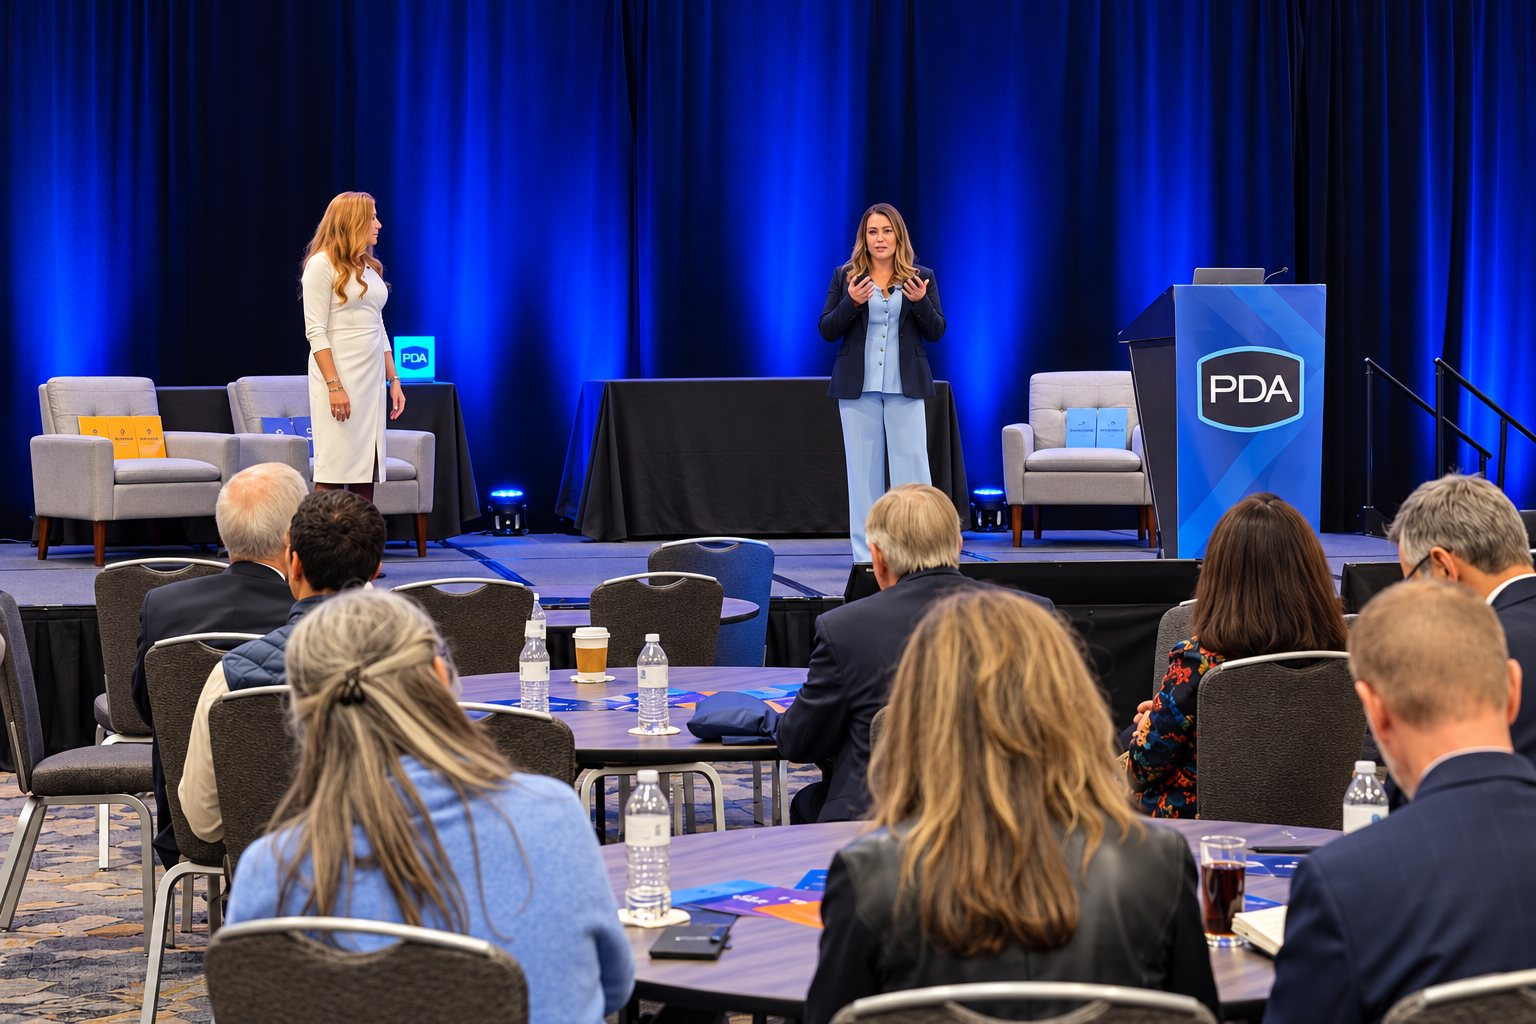
We developed the session around a question that sounds relatively straightforward: Do boards understand the perspectives their directors bring to the table?
The PDA’s 2026 Private Company Governance Report, developed with ASU’s New Governance Lab, gives us good reason to ask.
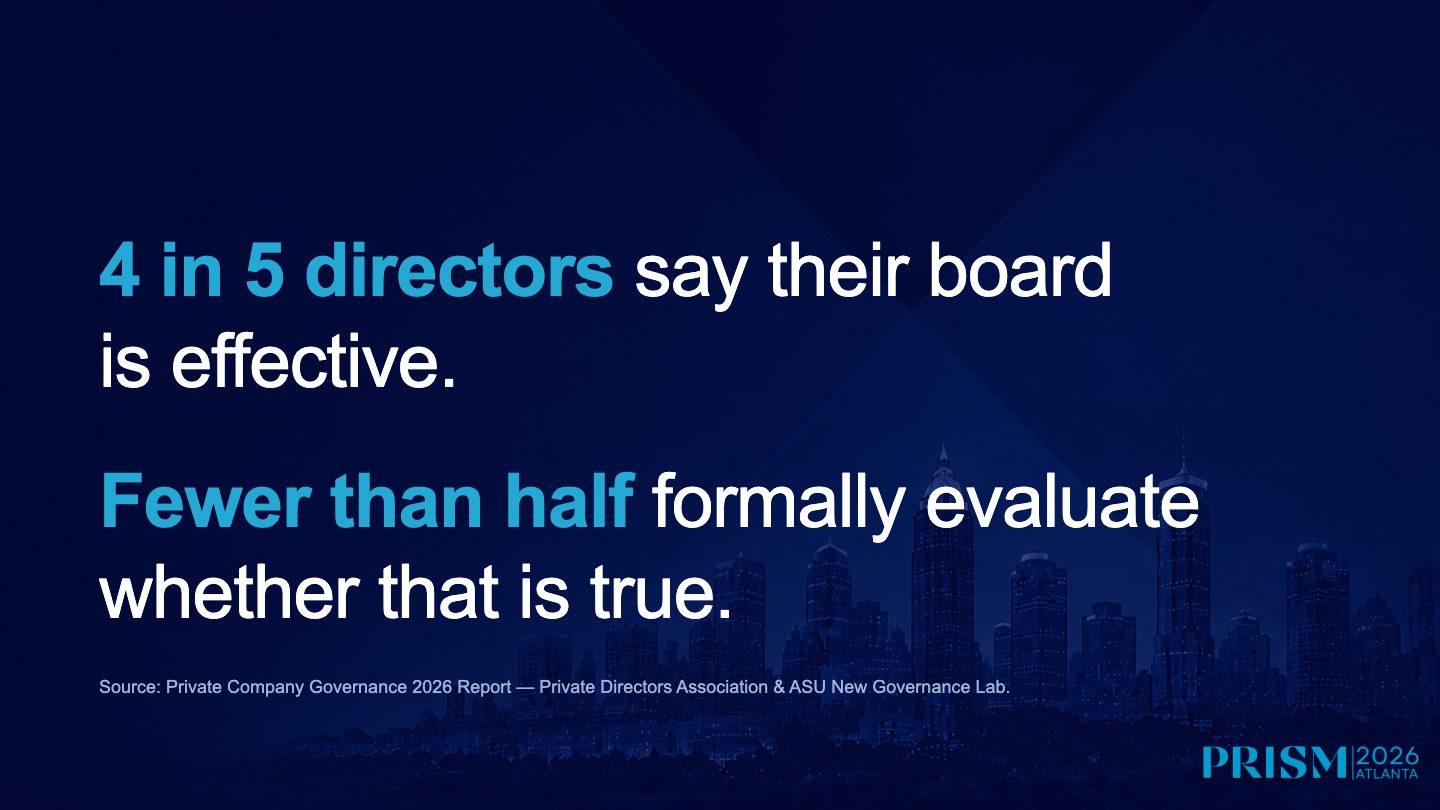
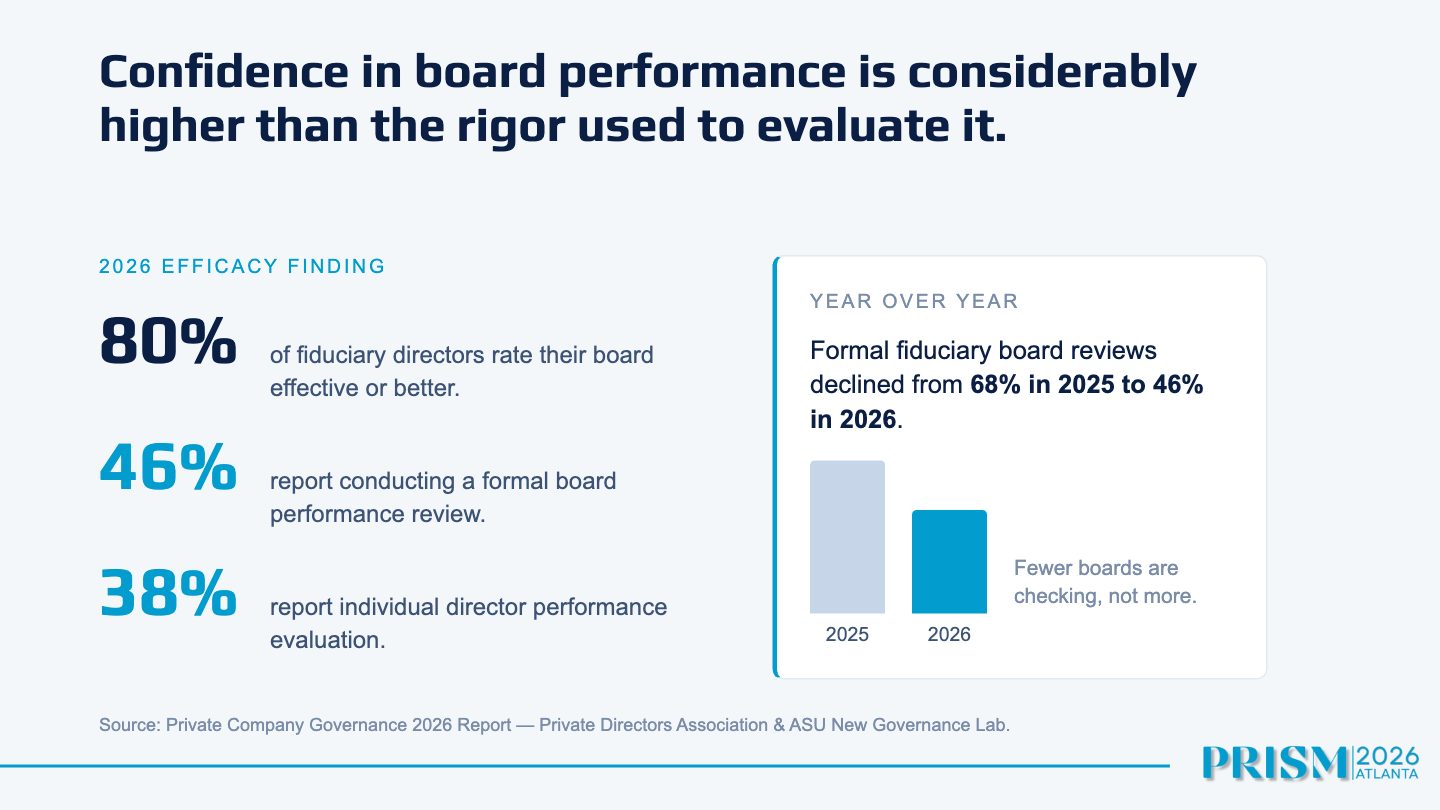
4 in 5 directors believe their boards are effective. Yet fewer than half formally evaluate that effectiveness. In fact, formal fiduciary board performance assessments declined from 68% in 2025 to 46% in 2026.
That’s a fairly significant confidence-to-evidence gap.
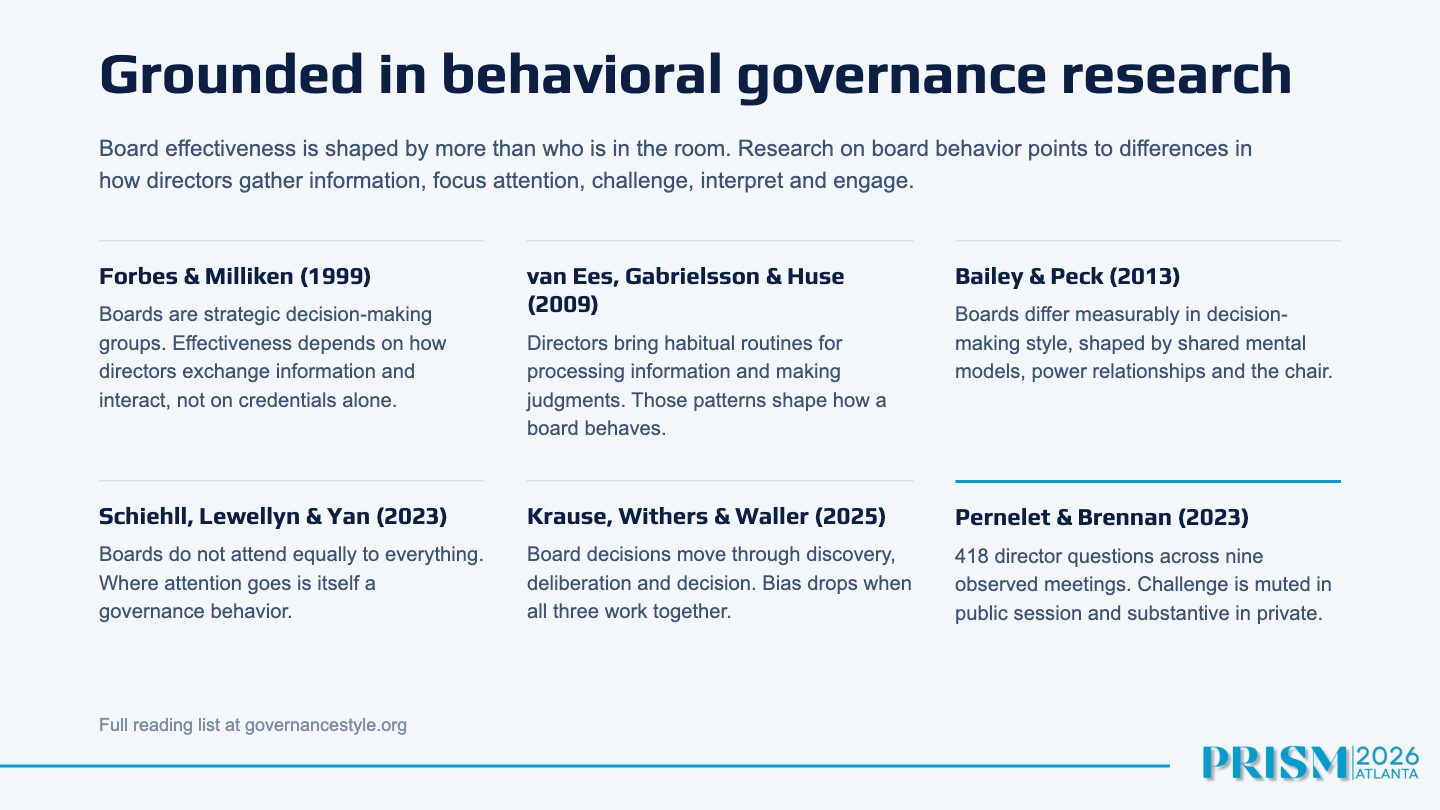
Board composition is usually discussed in terms of experience, expertise, independence, and networks. All important. But research into behavioral governance suggests that effectiveness also depends on how directors gather information, interpret what they’re seeing, challenge assumptions, and approach decisions.
We wanted to give directors a practical way to recognize those differences.
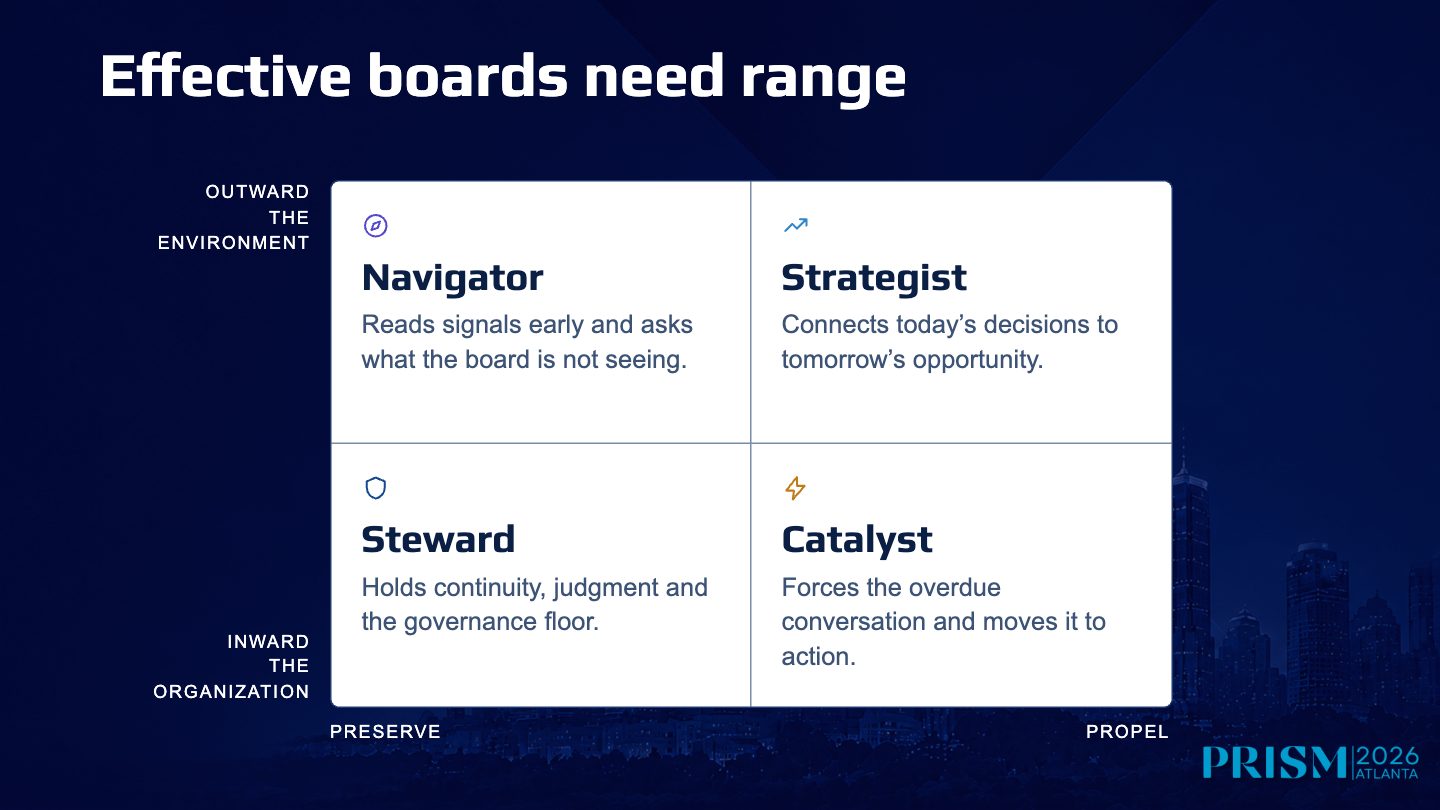
Our framework looks at 2 dimensions:
- Where you look for information: inward toward the organization or outward toward the broader environment.
- How you apply that information: preserving what matters or moving the organization forward.
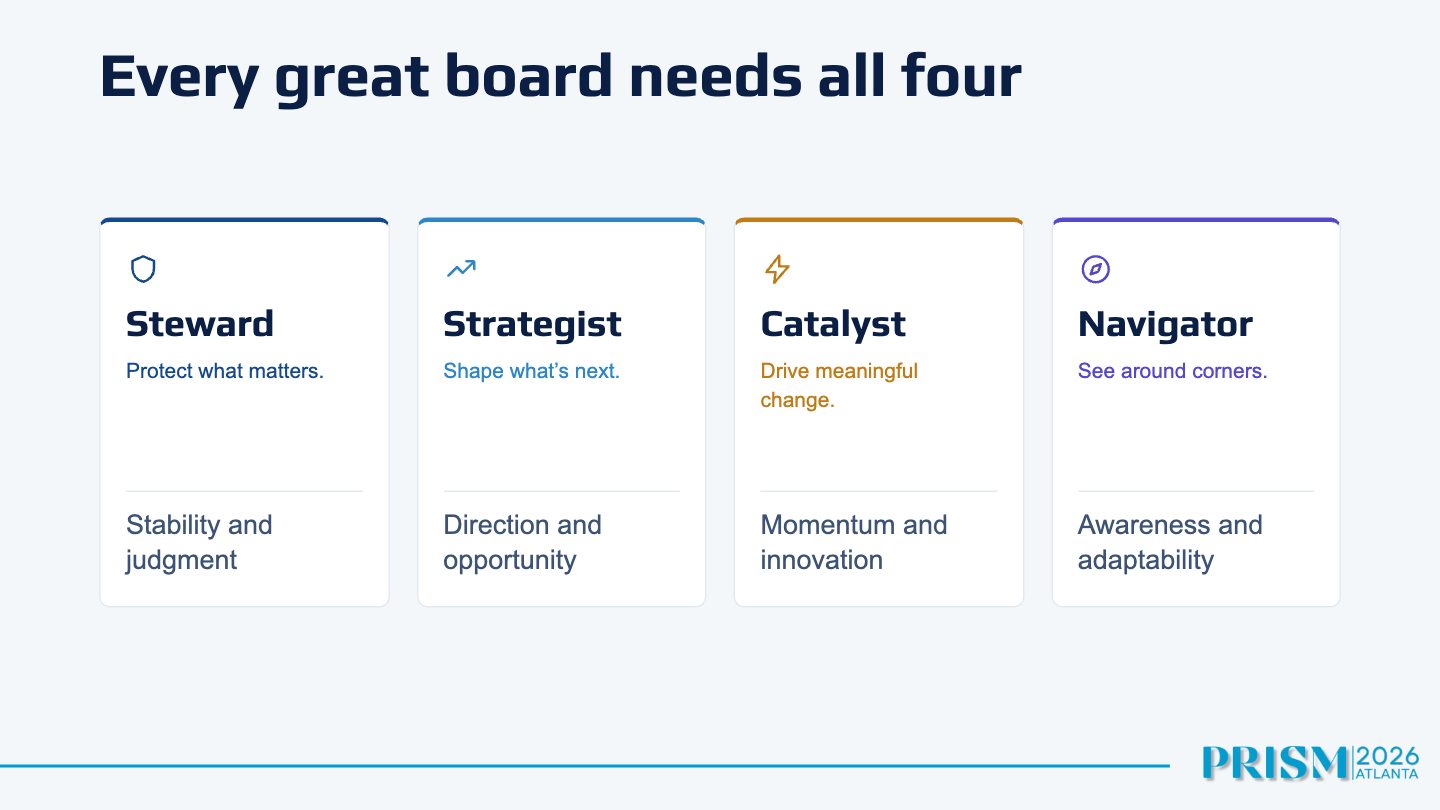
That produces 4 governance styles:
Navigator: Looks outward to identify emerging signals, dependencies, and risks the organization may be missing.
Strategist: Connects external developments and future opportunities to the company’s direction.
Steward: Focuses on continuity, accountability, and the foundations of good governance.
Catalyst: Challenges internal assumptions and pushes the organization toward meaningful change.
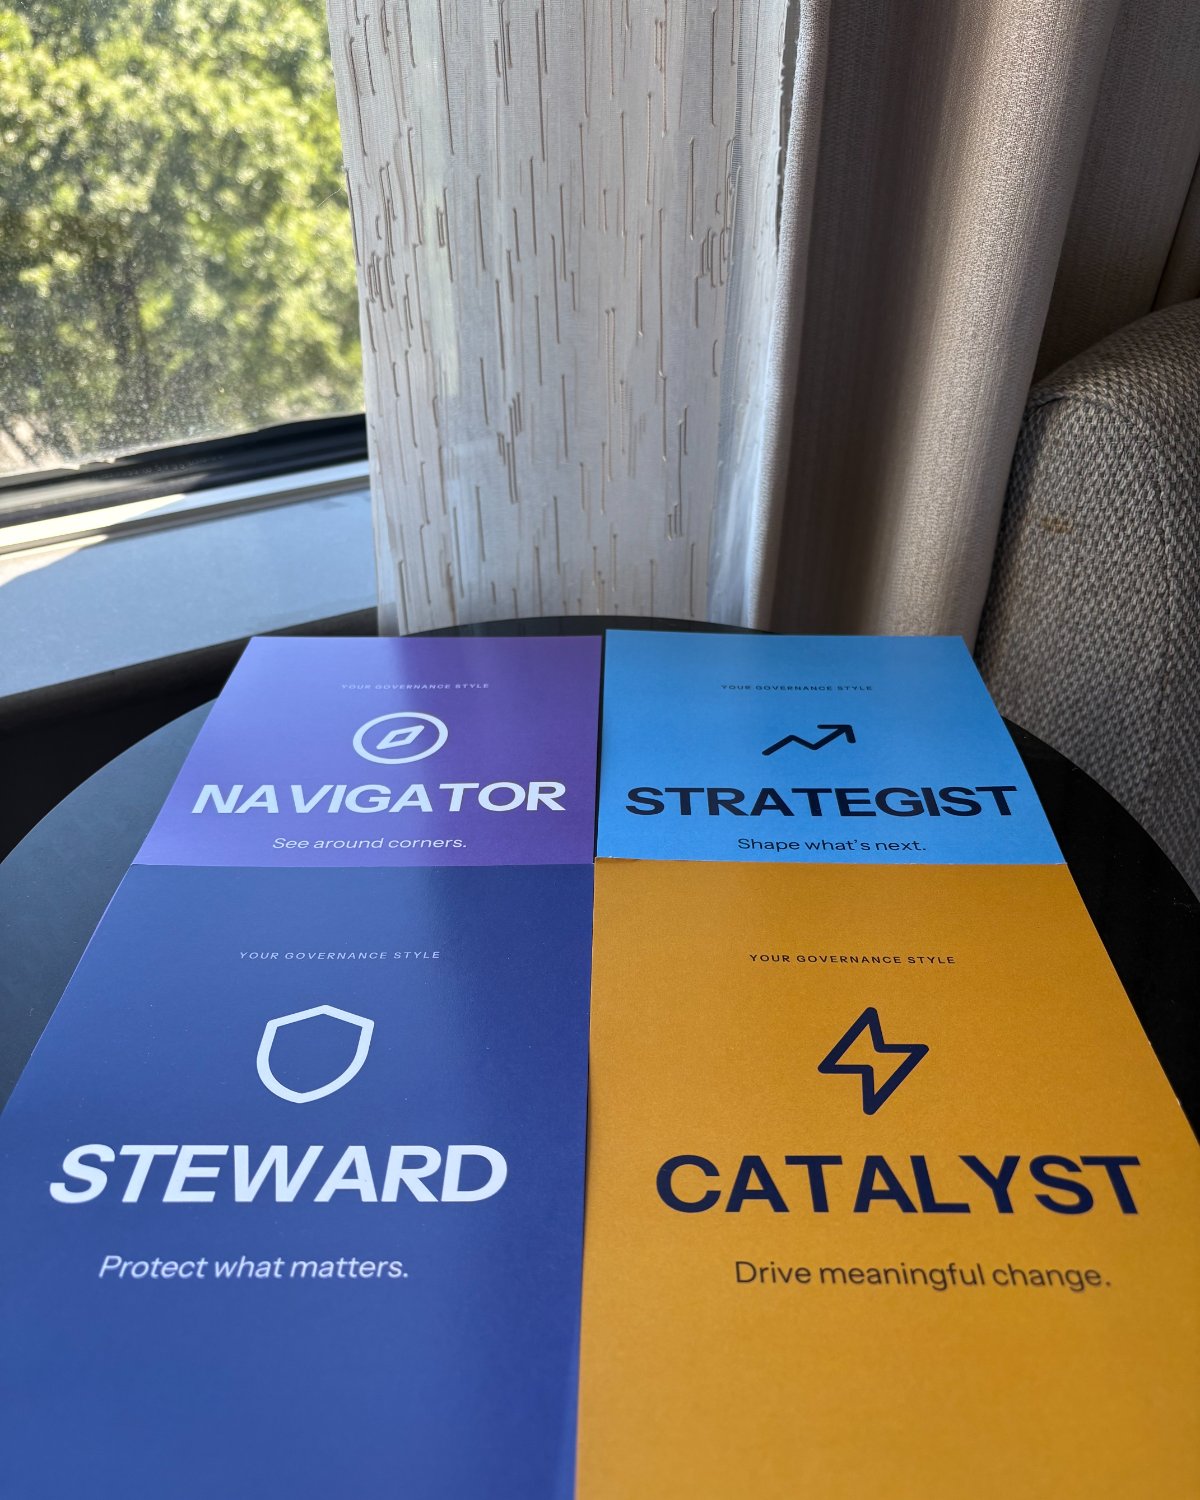
Most directors will recognize elements of several styles, but typically have a dominant orientation.
Curious which one you lead with? Take the governance style assessment at governancestyle.org.
The more interesting application is at the board level.
What happens when a board is heavily weighted toward one perspective? Who is challenging the strategic assumptions? Who is identifying what could disrupt the plan? Who is making sure the organization has the discipline to execute?
A board can have exceptionally accomplished individuals and still have meaningful gaps in how it processes information and makes decisions.
One of the questions we put to the room was simply:
What kind of boardroom are you sitting in?
The research raises some uncomfortable questions
In the second half of our session, we connected the archetypes to findings from the PDA research.
A few stood out.
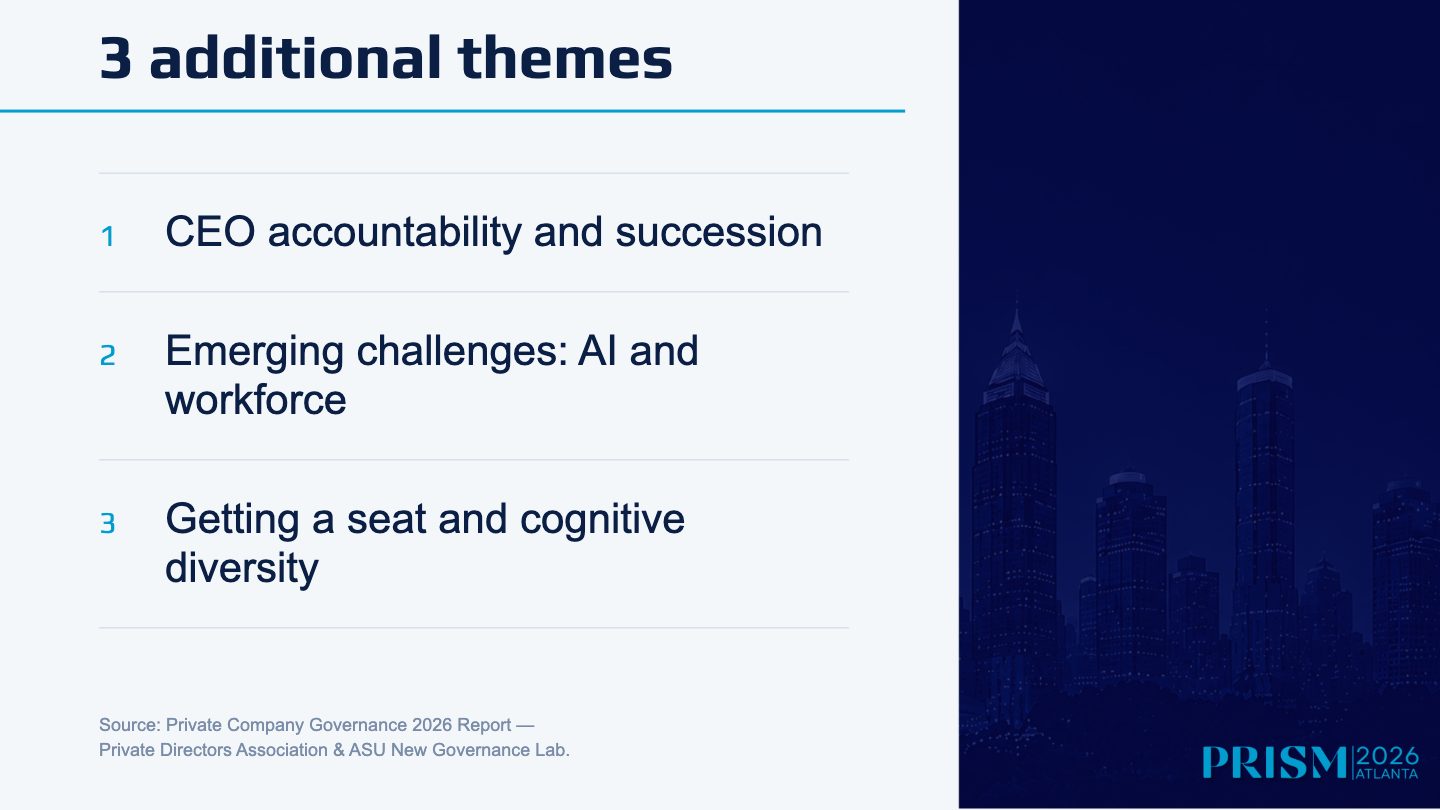
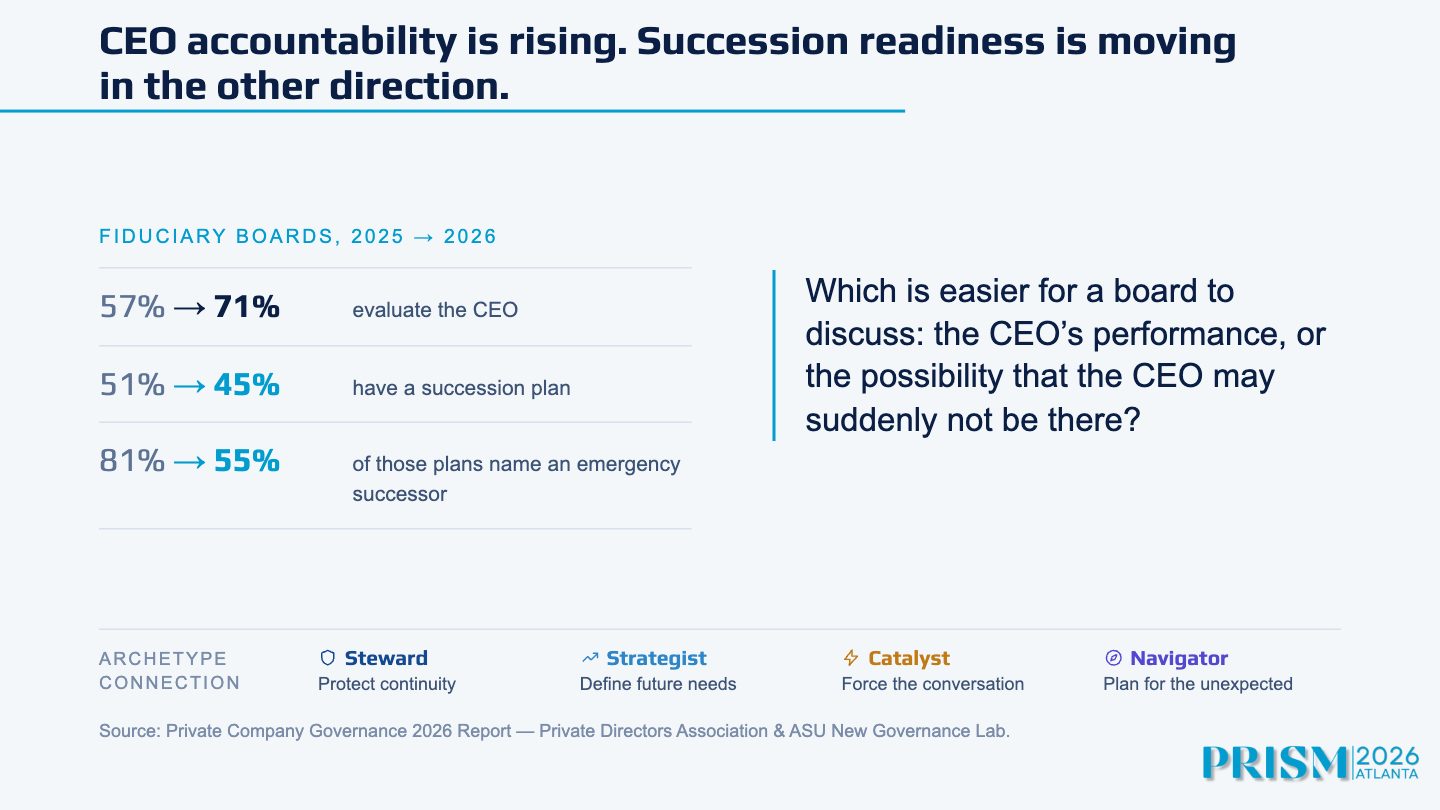
Succession: CEO performance evaluations increased from 57% to 71%, yet the percentage of fiduciary boards with a succession plan declined from 51% to 45%.
Are we spending more time evaluating the person running the business than preparing for the possibility that they may no longer be there?
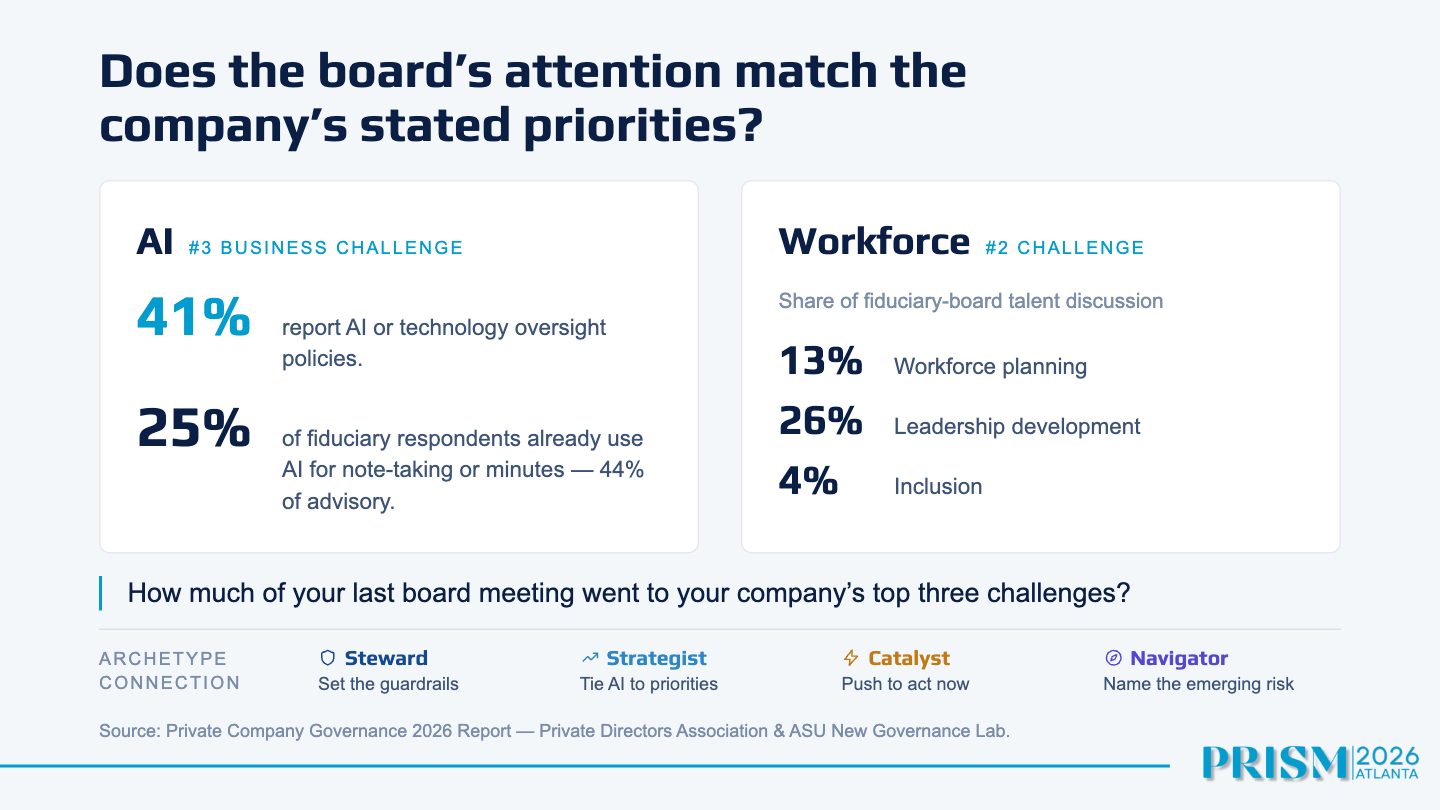
AI oversight: AI ranked as the third most significant business challenge, but only 41% of respondents reported having AI or technology oversight policies.
How much time does your board actually spend on the issues it identifies as most consequential?
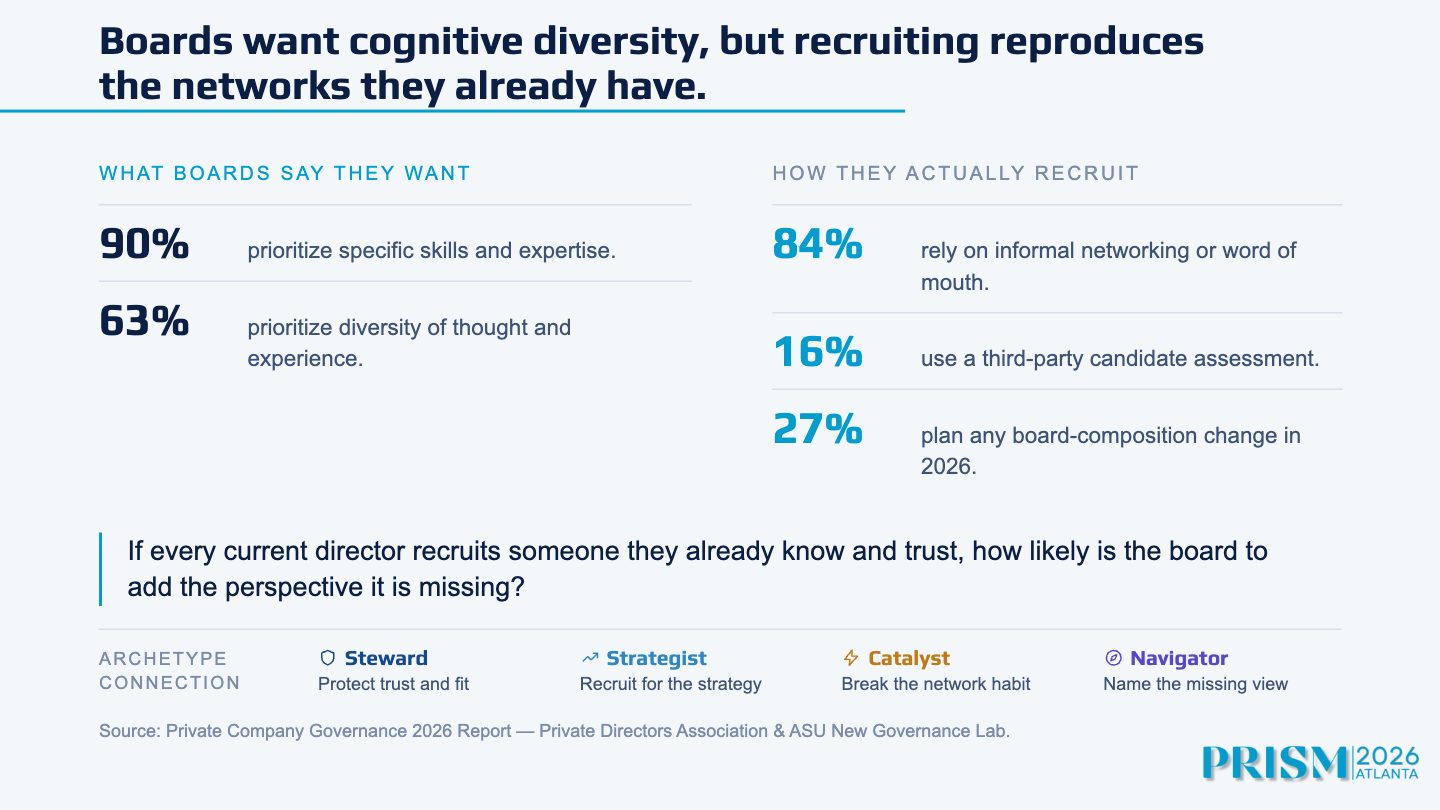
Board composition: While 63% prioritize diversity of thought, 84% still rely on informal networking or word of mouth for director recruitment.
If we recruit primarily from people we already know, how deliberately are we introducing perspectives we might be missing?
These are useful questions regardless of which governance style you identify with. In fact, comparing how different directors answer them is where the framework becomes most valuable.
3 things I took away from PRISM
Beyond our sessions, 3 themes kept surfacing in conversations with directors and speakers throughout the conference.
1. Boards need to spend more time governing strategy
There’s a familiar pattern in boardrooms: management develops a plan, brings it to the board, walks through the rationale, and the board approves it.
Sometimes with good questions. Sometimes with very few.
The keynote panel, Strategy, Scenario Planning, and Agility: Where Boards Make the Difference, brought together James D. White, Gary Dennis, Claudia H. Allen, and Milford McGuirt, and set the stage well for our Director, Defined session.
James offered an interesting framework, describing strategy as roughly 30% of the business, execution as 60%, and agility as 10%.
The board shouldn’t be managing execution. Its value is in shaping and challenging strategy, and understanding whether the company can adapt when conditions change.
Gary Dennis was particularly direct: “We don’t talk about strategy enough in the boardroom.”
That observation matters when you consider just how many pressures are converging on businesses.
James also described the board’s role as being “the parent in the room.” I liked that characterization. Management is understandably invested in the strategy it has developed. Directors need sufficient distance to evaluate it objectively, including when the argument for changing direction is uncomfortable.
Good governance requires the willingness to challenge a plan that everyone has already invested in.
2. Context is becoming a board-level capability
One of my favorite questions from the conference was:
How is the world seeing us, and how are we seeing the world?
There’s a lot packed into that.
Boards can become deeply familiar with the company’s strategy, internal performance, and operating assumptions while losing perspective on what’s changing around it.
They can also become so focused on what’s next that they overlook the institutional knowledge and historical decisions that explain how the company got here.
Both matter.
Gary Dennis spoke about the importance of understanding the customer and the front line, and ensuring the right skills are present around the CEO.
I’d extend that challenge to directors themselves.
How prepared are we to provide sound judgment in an environment we haven’t personally operated in?
Experience remains enormously valuable. But its value depends partly on our ability to recognize when the conditions that made that experience relevant have changed.
That requires intellectual curiosity, exposure to different perspectives, and a willingness to keep learning.
3. Risk and innovation are competing for the same decisions
This was probably the most consistent theme of the week for me.
Every strategy is built on a set of assumptions about what customers need, how markets will develop, where value will be created, and what capabilities the company will need to compete.
Those assumptions have a shelf life.
One exercise discussed at PRISM was to ask directors how they would kill the company.
It’s a provocative question, but a useful one. If you were a competitor, a new market entrant, or a disruptive technology, where would you attack? What would make the company’s existing advantages irrelevant? What would have to change for the current strategy to stop making sense?
Several directors expressed interest in spending more time considering worst-case scenarios.
I think that’s an important instinct, particularly when the purpose is to understand the decisions that would preserve strategic options.
There were also some fundamental questions about ambition: How quickly should we grow? How much should we invest? How much control are we willing to give up?
One quote from the conference captured the longer-term perspective particularly well:
“We don’t plan for quarters. We plan for quarters of centuries.”
What struck me across all these conversations is how closely risk oversight and strategic foresight are connected. A board needs to understand both what could threaten the business and what could make its current strategy obsolete.
And then there’s AI
The conversations at PRISM were particularly relevant given what was happening in the news this week.
An AI-powered security-testing tool was reportedly used in attacks targeting South Korean financial institutions. U.S. authorities disrupted China-linked infrastructure used for scanning and phishing against critical systems. Meanwhile, Anthropic expanded access to advanced cybersecurity capabilities for verified defenders and introduced a program supporting critical-infrastructure defense.
3 different developments, with a common governance implication.
What can a system actually reach once it’s deployed, and what authority does it have when it gets there?
This is becoming one of the more consequential questions for boards overseeing AI adoption.
When a security tool becomes part of the threat
CrowdStrike reported that an attacker used ARTEX, an open-source AI-powered penetration-testing tool, in a campaign targeting South Korean financial institutions.
The tool was developed for legitimate security testing. According to the reporting, it was used alongside commercial AI models to target peripheral banking systems. Its developer subsequently moved the project to closed source.
The story illustrates something important about increasingly capable AI systems.
The intended purpose of a tool tells us relatively little about what it can do once given access to real environments.
Companies are introducing AI into workflows that involve source code, internal systems, customer information, financial processes, and operational decision-making.
The governance question becomes progressively more consequential as systems move from recommending actions to drafting, accessing, modifying, approving, and ultimately acting.

Each step changes the nature of the authority being delegated.
For technology providers, that means being able to demonstrate where authority ends, what activity can be observed, and how intervention works.
For companies deploying these tools, it means understanding which systems and data they can reach, what actions they can take independently, and who is accountable for those decisions.
This belongs in the governance conversation well before an incident occurs.
Critical infrastructure offers a useful lesson
This week, U.S. authorities also announced the seizure of domains supporting Microscan and FishHub, tools allegedly associated with China-linked activity targeting critical infrastructure.
The NSA separately released zero-trust guidance for operational technology environments.
These environments expose the practical difficulties of security governance: legacy systems, complex dependencies, limited opportunities for downtime, and consequences that extend well beyond a technology incident.
Most private companies aren’t operating power grids or airports.
But they do have business-critical systems, fragile dependencies, legacy technology, and processes that cannot be interrupted without consequences.
The lesson carries across sectors.
Understanding what is connected, limiting unnecessary access, and testing the decisions required during a disruption remain fundamental capabilities.
And those decisions need to be practiced in the context of how the organization actually operates.
AI is expanding the capability of defenders, too
Anthropic’s expansion of its Cyber Verification Program and the launch of Anthropic Cyber Mission are encouraging developments for security teams.
Advanced AI capabilities could allow organizations to identify vulnerabilities, investigate incidents, and respond to threats with far greater speed.
But increasing the capability of a system also increases the importance of defining its operating boundaries.
Where can it operate? What does it need approval to do? What needs to be recorded? Who can intervene? How does the organization know whether the system is behaving as intended?
These are management questions with direct implications for board oversight.
And they become especially important when organizations begin relying on AI to perform work previously carried out by people.
Making governance practical
We explored some of these issues directly in our Building Board AI Fluency masterclass with Vela Board Advisors, using an interactive iluminr simulation to put directors into a realistic AI governance decision.
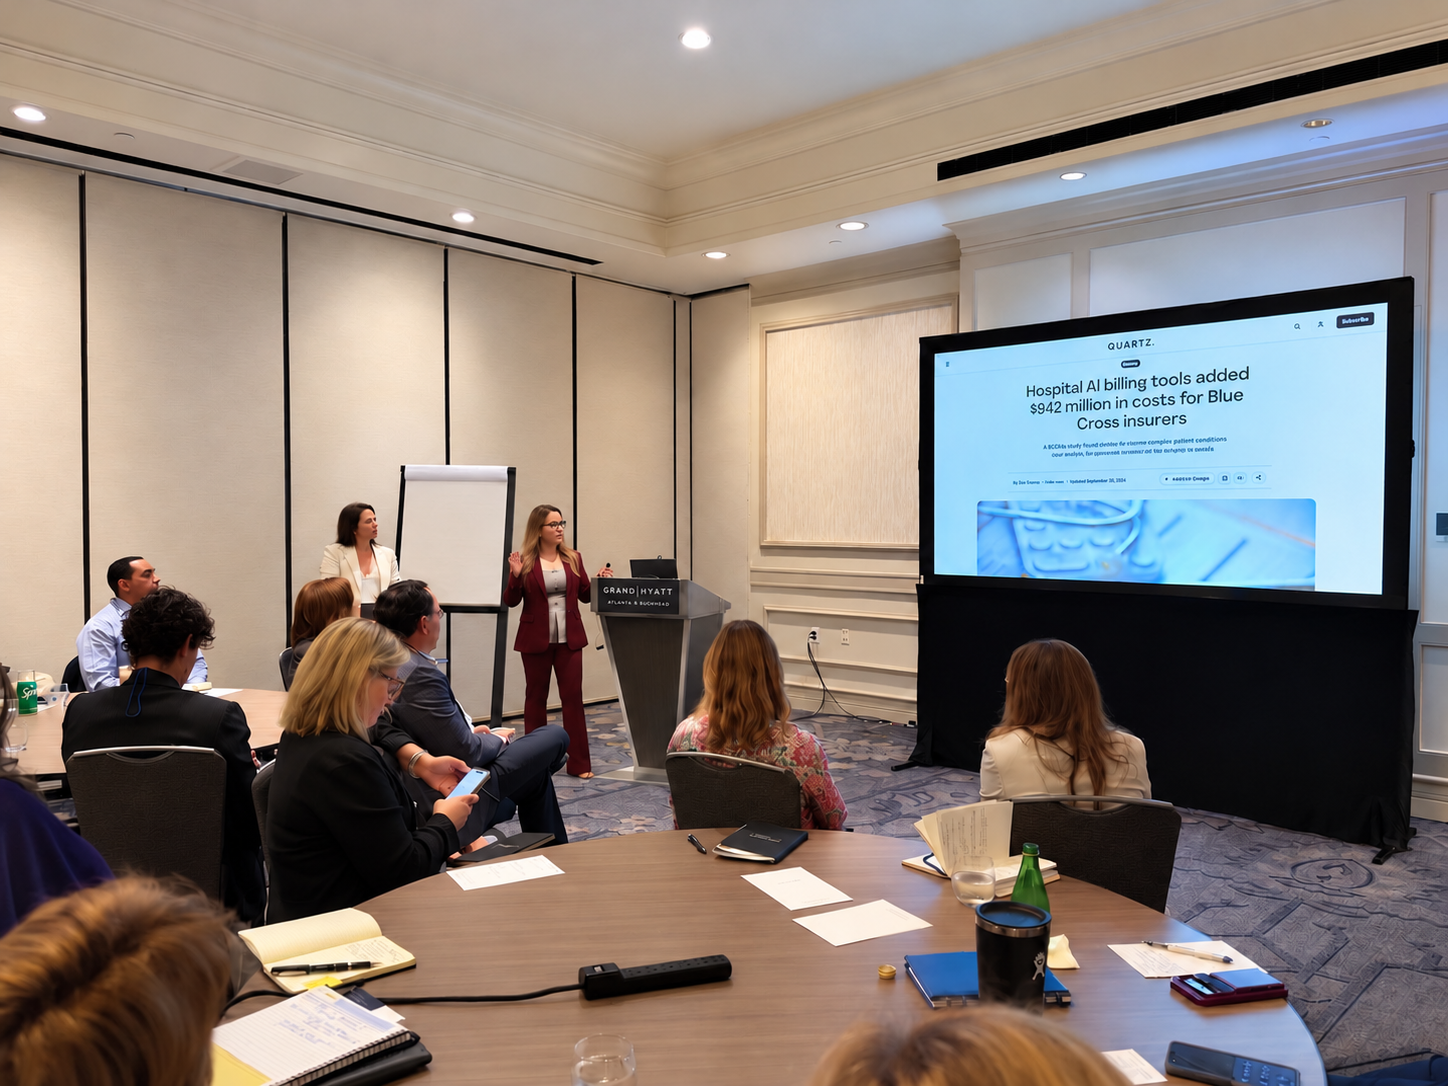
The premise was straightforward: directors were presented with an AI-related business decision, had to consider the information available, weigh competing priorities, and determine what the board should do.
Because that’s ultimately where governance is tested.
In our Director, Defined session, we explored how individual perspectives influence the questions directors ask.
Across the broader conference, we discussed the importance of strategic challenge, context, adaptability, and informed judgment.
And in the AI governance masterclass, we moved from talking about oversight to making decisions with incomplete information and real consequences.
I see a clear connection between all 3.
Boards need the right range of perspectives, a shared understanding of the environment in which the business operates, and the ability to apply their judgment to decisions that matter.
The technology will continue to change. So will the risks, opportunities, and assumptions underpinning business strategy.
The more interesting measure of governance effectiveness is whether the board can recognize when a consequential decision is emerging, ask the right questions, and act while there are still meaningful options available.
Beyond the Boardroom
The question of assumptions extends well beyond governance. It also shapes how we understand emerging technologies, recognize market opportunities, and decide where to invest.
We’ve been exploring two related shifts at Eudai this week.
In The Trouble With Calling Everything Superintelligence, we examine what happens when the language used to describe a technology gets ahead of its actual capabilities. Category names influence expectations, purchasing decisions, and ultimately what markets are prepared to trust. When terminology becomes detached from reality, it becomes harder to make informed decisions about where the opportunity really lies.
In The Portfolio Economy Is Taking Shape, we look at another assumption worth revisiting: that careers, companies, and value creation should be organized around a single primary commitment. As portfolio careers and more flexible business models gain traction, the implications extend to how companies access expertise, how executives build careers, and how new ventures emerge.
Both pieces return to something that came up repeatedly at PRISM: the importance of examining the assumptions behind our decisions.
Whether we’re governing a company, evaluating a technology, or considering a new business model, the quality of our decisions depends on how well we understand the environment we’re operating in and how willing we are to reconsider what we think we know.